AI on infrastructure you own, under the controls your security team require
Four AI products: Portainer-Run for the AI-built apps your people are shipping, Portainer-Command for letting AI safely operate your Kubernetes fleet, Portainer-AiGrid for private corpus retrieval on compute you already own, and Portainer-AiSecure for finding the weaknesses in your network before attackers do. The first three run on your Kubernetes platform, use your existing RBAC, and write to the same audit trail. Portainer-AiSecure runs self-hosted inside your network, with its attacks directed by a model you run.
Each product stands alone. Start with whichever AI conversation is loudest this quarter and add the others as they come up.
A toolbox of solutions for your AI problems.

Portainer-Run
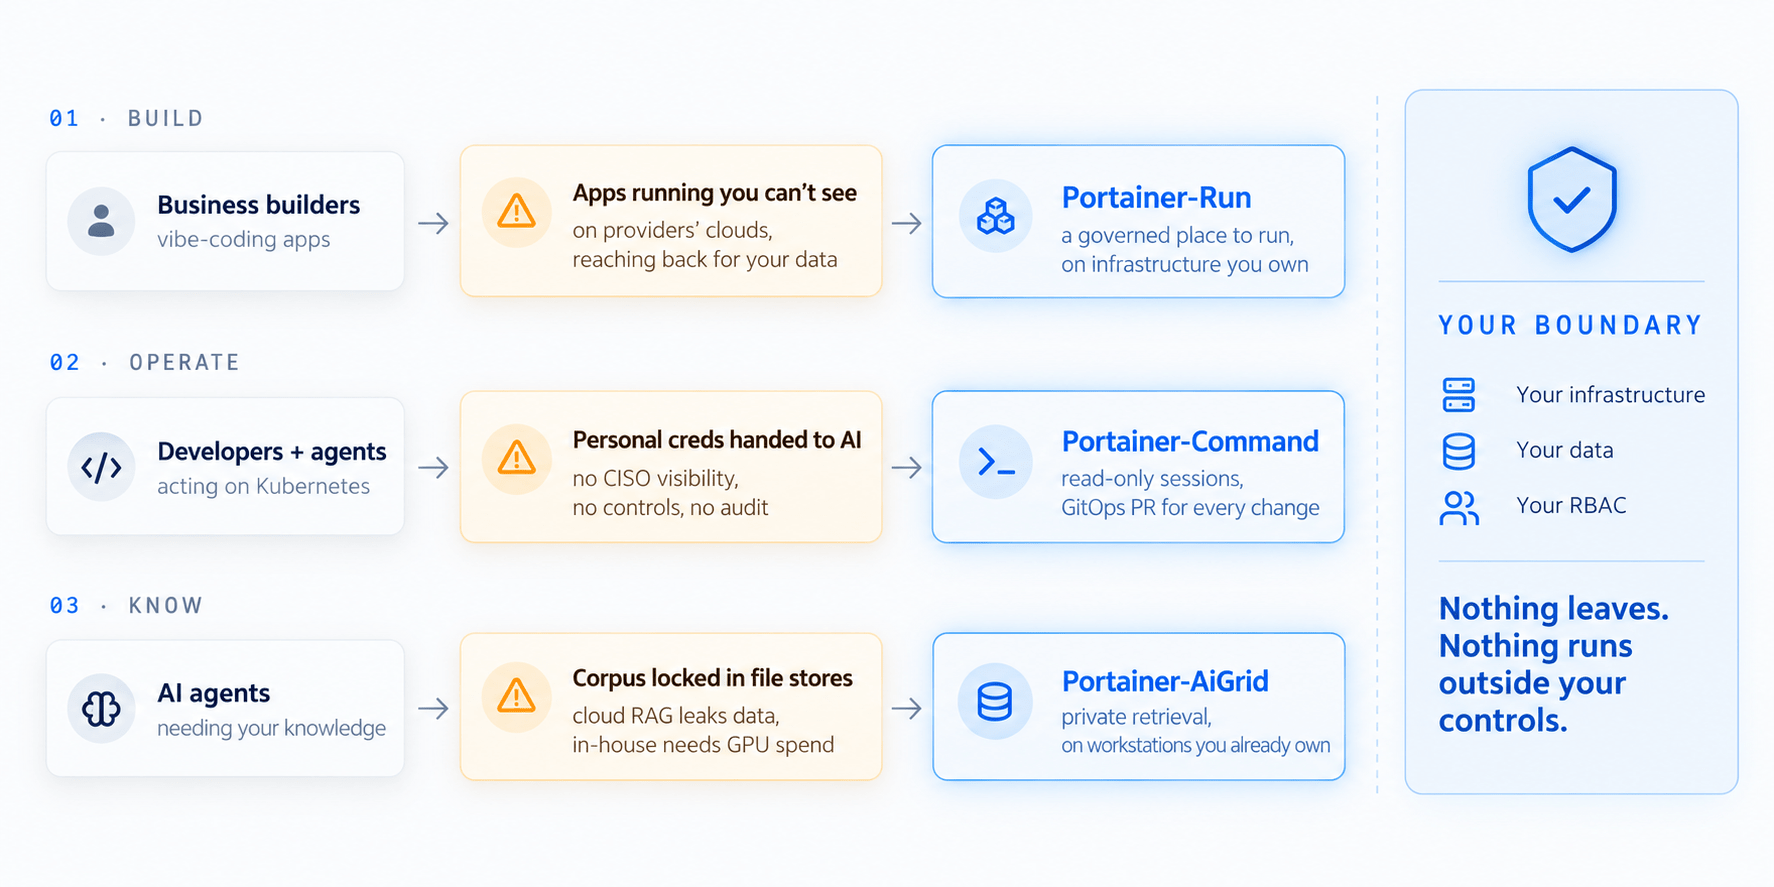
The governed landing zone for AI-built business apps. Direct deploy from Claude and other MCP-aware AI clients; source from anywhere else lands via zip upload or Git commit. Runs on your Kubernetes platform under the RBAC and audit trail your security team already require.
- Direct MCP deploy from Claude Desktop, ChatGPT Desktop, Cursor
- Zip upload or Git commit for source from any other AI tool
- Isolated Kubernetes sandbox per app
- Business users never see a cluster
- Everything is a Git commit
Portainer-Command
A governed, audited workspace where developers use an AI agent to deploy and manage workloads on the clusters you already manage with Portainer. An MCP gateway: agents get expiring read-only sessions and propose changes as GitOps pull requests; humans approve, Portainer applies.
- Read-only sessions with rationale + TTL
- AI proposes, human approves, GitOps applies
- Full audit log across every agent
- Runs independently of your existing pipelines
Portainer-AiGrid
Turn your document corpus into a private, citable retrieval endpoint any AI agent can query. Runs on idle workstations you already own; no per-seat pricing, no six-figure enterprise-search invoice.
- Idle-hours OCR + embedding on your fleet
- Retrieves, never generates: no fabricated answers
- Every result carries filename and page
- Documents never leave your bucket
Portainer-AiSecure
Find the weakness in your network before the hackers do. A coordinator in your core directs an agent in every network segment to run simulated attacks and hunt systems that are already compromised, directed by a self-hosted open-weight model that you run. Built on MisterShell.
- Simulated attacks from inside each network segment
- Hunts systems that are already compromised
- Attacks directed by a model you host
- Core, Kubernetes, or Edge delivery
Nothing new to onboard
Portainer-Run, Portainer-Command, and Portainer-AiGrid are add-ons that run on Portainer Business, the same control plane you may already use to manage your Kubernetes platform. They don't replace anything: they build on Portainer's existing RBAC, GitOps, and audit trail. Portainer-Command runs independently of your existing pipelines, with its own GitOps repository. If you already run Portainer, there's no new access path and no new security review. If you don't, Portainer Business is included and can be stood up as part of the installation. Portainer-AiSecure is the exception: it is built on MisterShell, a self-hosted privileged access and fleet intelligence platform, and runs on its own.
Your questions, answered directly
What are Portainer's AI solutions?
Four products, each aimed at a specific AI problem. Three are add-ons to Portainer Business: Portainer-Run for AI-built apps that need a governed place to run, Portainer-Command for AI agents that need access to Kubernetes without personal credentials, and Portainer-AiGrid for AI agents that need to answer from your document corpus rather than training data. Portainer-AiSecure, built on MisterShell, uses a self-hosted model you run to simulate attacks from inside your network and hunt systems that are already compromised.
Do I have to buy all four?
No. Each stands alone. Most start with whichever AI conversation is loudest this quarter.
Where do the add-ons run?
On your Kubernetes platform, wherever it lives: cloud, on-prem, edge, air-gapped. Portainer-AiSecure runs self-hosted inside your network, either on its own (Core), on KubeSolo (Kubernetes), or as a full bundle for edge locations (Edge).
Do I need to already run Portainer?
No. Portainer-Run, Portainer-Command, and Portainer-AiGrid are add-ons that run on Portainer Business, which is included with each product and can be stood up as part of the installation. If you already run Portainer Business, you enable an add-on and it uses your existing RBAC and audit trail, with no new access path. Portainer-Command keeps its own GitOps repository, separate from your existing pipelines. Portainer-AiSecure does not need Portainer Business at all.
How does it differ from Backstage or Port?
Backstage and Port are internal developer platforms; the primary users are engineers who already know Kubernetes and Git. The add-ons cover three specific AI problems; each product has a self-service surface that requires no Kubernetes knowledge, and each is callable by AI agents through MCP.
Is data leaving our environment?
No. Workloads run on your Kubernetes platform, documents stay in your bucket, agent traffic terminates inside your boundary, and Portainer-AiSecure's attacks are coordinated by a model you host.
See it run on infrastructure you already operate
We will walk you through the product that maps to your current AI conversation, on a live governed environment, and show you exactly what it takes to stand it up in yours.